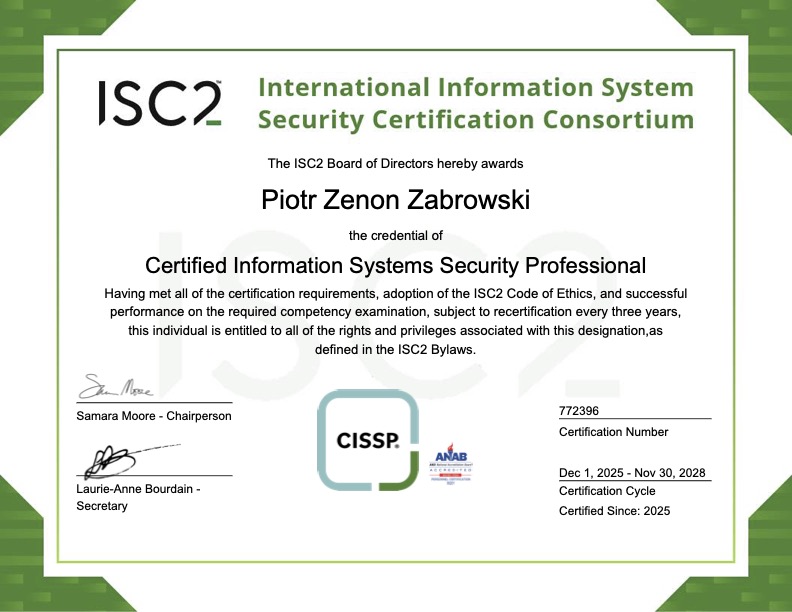
CISSP
Earned in 2025. CISSP covers the full breadth of the profession, which makes it the common language when talking to auditors, boards and other security leaders.
Updated
What the exam actually covers
CISSP is ISC2's eight-domain body of knowledge. Security and Risk Management carries the most weight at 16%; Security Architecture and Engineering, Communication and Network Security, Identity and Access Management, and Security Operations sit at 13% each; Security Assessment and Testing is 12%; Asset Security and Software Development Security are 10% each. It's a 3-hour computer-adaptive exam, 100-150 questions, pass mark 700/1000.
Domains and where they show up in my work
| Domain | Applied in |
|---|---|
| Security and risk management | CISO advisory, roadmap and board reporting |
| Asset security | Data classification for cloud and AI systems |
| Security architecture and engineering | Cloud architecture reviews, threat modeling |
| Communication and network security | Segmentation and egress control design |
| Identity and access management | Entra ID, Conditional Access, PIM work |
| Assessment and testing | Assessment methodology and evidence standards |
| Security operations | Detection coverage, IR readiness, playbooks |
| Software development security | SDLC threat modeling and AI feature review |
Related
SSCP
SSCP (ISC2, 2021): hands-on operational security practitioner credential covering access controls, monitoring and incident response.
Cloud security
Multi-cloud security practice: landing zones, identity, posture management, MITRE ATT&CK-aligned detection engineering and CIS hardening baselines.
CISO advisory
Security leadership support for organisations without a full-time CISO: strategy, roadmap, board reporting and vendor decisions.
From Threat Modeling to a General Principle
Thoughts on threat modeling
Cloud architecture review
Design-stage review of cloud and hybrid architecture: trust boundaries, identity model, segmentation, key management and detection design.
Threat modeling
Facilitated STRIDE threat modeling on your real architecture, plus the templates and coaching to keep teams doing it without me.